After attackers used credentials stolen from GMO's Onamae.com Desktop Cloud to drain FX accounts, GMO asked Japan's government on October 24, 2026 to invoke active cyber defense. What the new police neutralization clause allows against non-state criminals, the approval steps, the international-law problem with servers abroad, and what is likely to happen.
The Brotli out-of-bounds write called Node2Shell and HTTP2Shell (CVE-2026-111497) also reaches the Python Brotli packages and curl builds with Brotli when --compressed is used. On a Windows 11 PC I checked that Python decodes br responses whatever it asks for, that pip-audit now flags it, and that Git for Windows as of October 24 shipped the unpatched Brotli (fixed in 2.56.0.windows.4 on October 26), then updated Node.js.
Using Python, NPB records and the MLB Stats API, I put Hideki Matsui's ten Yomiuri Giants seasons and ten MLB seasons on a league-relative OPS+ scale, compared him with Sadaharu Oh, Shigeo Nagashima and later Giants cleanup hitters, and broke down his MLB WAR and pitch-level swing data.
Ruby 4.0.9, 3.4.12, and 3.3.13 (October 23, 2026) fix the Onigmo regex bugs behind GitLab's CVE-2026-89078, CVE-2026-93577, CVE-2026-97229, and CVE-2026-110264. Any Ruby app that builds a Regexp from outside input should upgrade. Five Ruby versions built under WSL2 show the unpatched ones crashing on the fix PRs' test patterns.
Two days after the php2shell fixes, PHP disclosed CVE-2026-115560 on October 23, 2026, an RCE the October 21 releases do not fix. The three conditions an app must meet, why servers that already set session.upload_progress.enabled=0 need nothing more, what PHP has not published yet, and how to grep your own code.
The 28th CGPM adopted Resolution 5 on October 15, 2026, allowing UT1 and UTC to drift up to 3,600 seconds apart. The text matches January's Draft Resolution C. Why sources say "several centuries" or "several millennia", and what ITU-R and others still have to do before it takes effect.
Nova Anime AM, CottonAnima, AMIXA2.9B, and JANIMA 2.9B tested on an M1 Max 64GB in ComfyUI with an Anima-Base character LoRA remapped to 40 blocks. All four kept the hairstyles, but Kei's red ribbon tie turned navy in portraits. Also compares default style, background density, i2i, and speed.
I ran the latest 2B versions (as of October 21) of Hikari, AnimaIka, Hotaru Blend, Cat Tower, CapAnima, RDBT, and AnimaYume in ComfyUI on an M1 Max 64GB, using the same prompts, seed, and character LoRA as Anima-Base v1.0. All seven got the hairstyles right, but only RDBT kept Kei's ribbon tie red in both full-body and bust shots, and RDBT turned two characters into four. Default style, background density, i2i, and generation speed are compared too.
I rechecked the latest versions of the Anima derivatives from my June list, plus Civitai's top 40 Anima checkpoints by monthly downloads, as of October 21, 2026. Which 2B models were updated, which moved to 2.9B, and why the two 3.8B models are built differently.
V4bel's Infinity Core is six bugs in Linux kernel core code (timers, signals, futex, MM, scheduler, SLUB). They were introduced anywhere from 5.7 to 7.2, so Debian 12/13 and stock Ubuntu 24.04 only get the Timer bug, while RHEL picked up Futex and Signal through backports. Per-CVE introduced versions and distro status as of October 22, 2026.
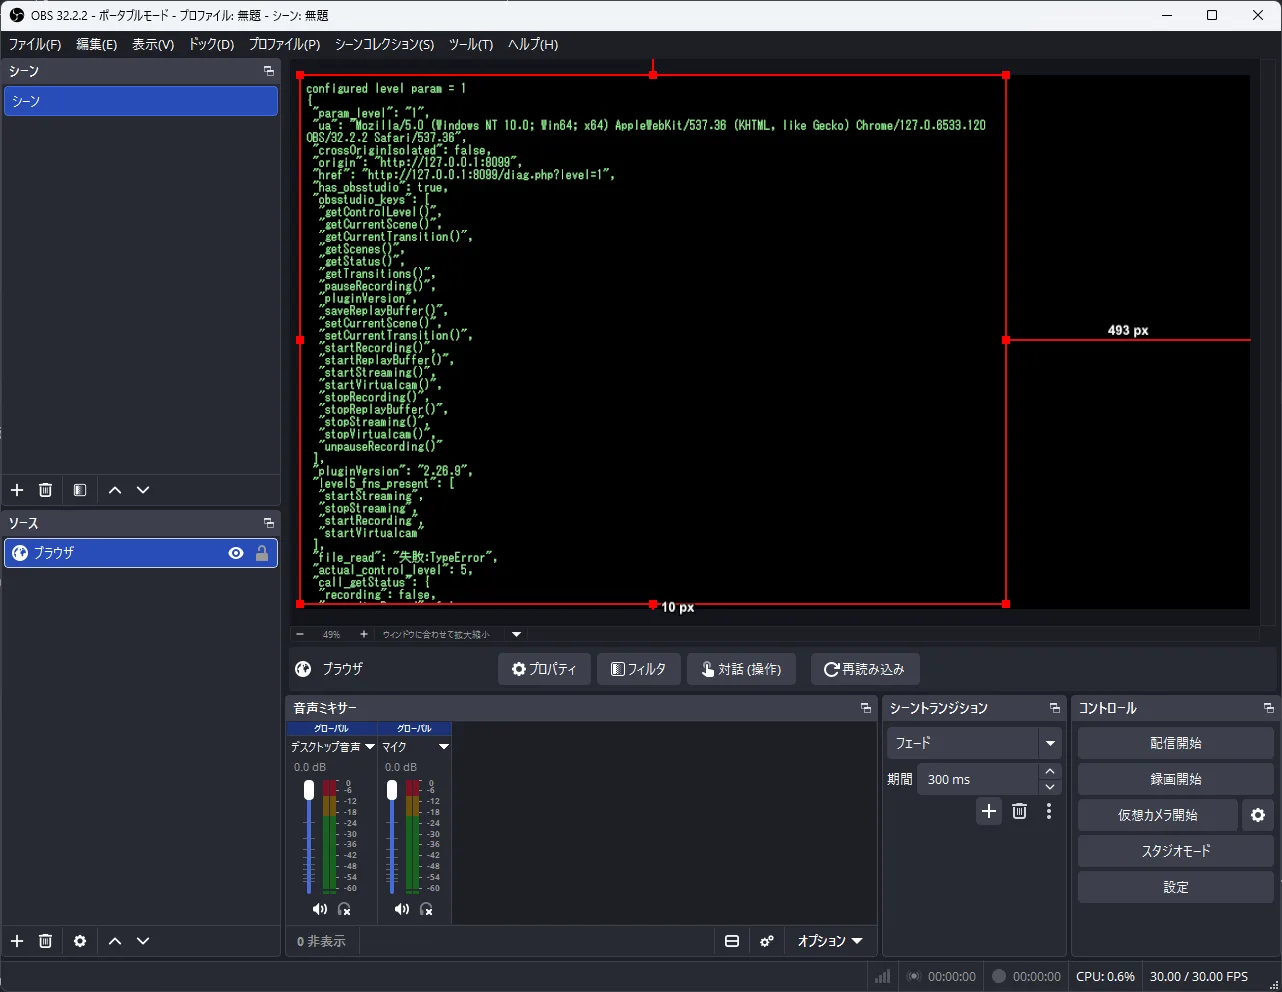
I tested what malicious pages can execute inside OBS Studio's browser source across permissions 0 to 5, obs-websocket, and the disabled CEF sandbox on Windows 11.
On October 21, 2026 PHP patched two unauthenticated RCE flaws (php2shell, CVE-2026-109618/109619). Hours later a self-published page claimed RCE and memory-safety bugs still survive on the patched 8.5.12. Which claims are confirmed, which are unfiled, and what server admins should actually do.