Registering a WebAuthn security key in phpMyAdmin fails with Internal error: TypeError when the fallback CustomServer is active. CustomServer stores raw 16-byte AAGUID values in JSON without text encoding, and json_encode() fails on invalid UTF-8. Verified in a local Docker lab; patched in upstream development branches in September 2026.
We tested the phpMyAdmin 5.2.3 WebAuthn 2FA signature bypass PoC in a local Docker lab. While the fallback CustomServer accepted arbitrary signatures, official tarball and Docker distributions bundle webauthn-lib and reject forged signatures with Invalid signature. Breakdown of vulnerable install paths with Composer test runs.
Following a solve of the PHP 8.4.26 CTF challenge 'Steal My Bitcoin', author KillaBoi released a standalone Python PoC tested on Alpine. Here is a teardown of how the chain triggers the session.upload_progress UAF, leaks addresses via session cookies, and hijacks HashTable cleanup into zif_system.
A version-by-version guide to breaking changes in PHP 5.3 through 8.6 (scheduled for November 2026) covering internal functions, argument handling, and namespaces where silent return value differences occur without syntax errors.
Two days after the php2shell fixes, PHP disclosed CVE-2026-115560 on October 23, 2026, an RCE the October 21 releases do not fix. The three conditions an app must meet, why servers that already set session.upload_progress.enabled=0 need nothing more, what PHP has not published yet, and how to grep your own code.
On October 21, 2026 PHP patched two unauthenticated RCE flaws (php2shell, CVE-2026-109618/109619). Hours later a self-published page claimed RCE and memory-safety bugs still survive on the patched 8.5.12. Which claims are confirmed, which are unfiled, and what server admins should actually do.
Japanese Prime Minister Sanae Takaichi urged PHP patching on X on October 21, 2026, and took her own website offline. The backstory, from the proposal PDF and official records: her 2018 cybersecurity book from PHP Institute (no relation to the language), the LDP proposal she signed, how it led to Japan's active cyber defense law, and two doctors in a row as Digital Minister.
When the php2shell patch arrived without Remi repository updates, we tested compiling php, php-fpm, and opcache.so from official source in an AlmaLinux 9 container, verified zero-downtime USR2 reloads, bypassed docker kill signal traps, and configured RPM exclusions.
A PHP core developer and GMO Flatt Security say disabling session.upload_progress does not stop php2shell. The PHP fix shipped on October 21, 2026 (8.5.12, 8.4.27, 8.3.36, 8.2.35): where to get it and the 8.1-and-older patches, status per distribution channel, how to apply it on shared hosting, apt, dnf, and Docker, and which services went offline.
PHP will ship fixes for two critical CVSS 9.2 bugs on October 21, 2026 at 14:00 UTC. Leaks call them php2shell (CVE-2026-109618/109619) and tie at least one to session.upload_progress, which is on by default. How to turn it off on shared hosting, php.ini, .htaccess, and .user.ini, and what is official versus leaked.
CVE-2026-114509 / GHSA-f9x3-7vq9-cph6 (CVSS v4.0 9.2): Laravel's built-in token guard on MySQL/MariaDB authenticated a non-string api_token as an existing user. How to check config/auth.php, which laravel/framework versions are fixed (12.68.0, 13.29.0, and the unlisted 11.56.1), and why MySQL matches the token column against 0.
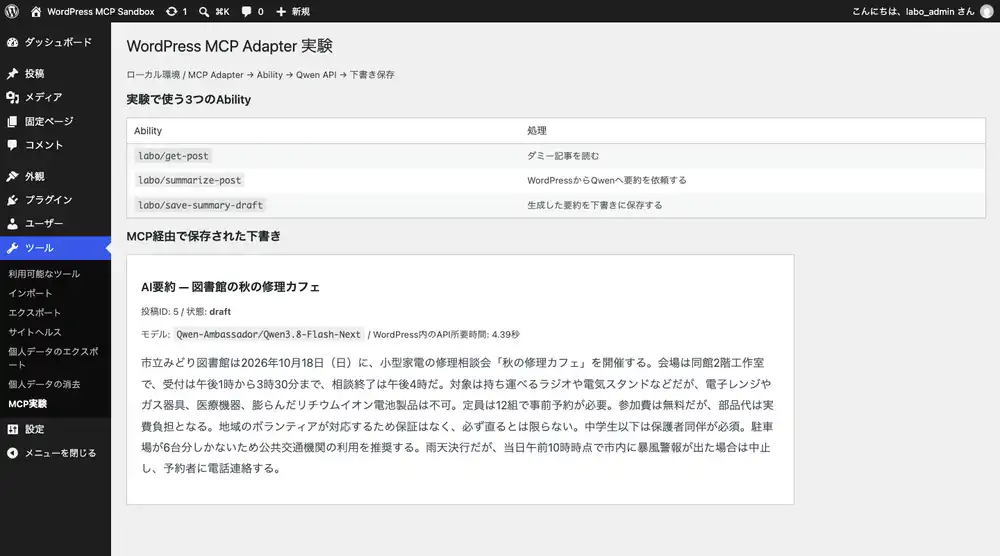
M4 Mac Docker test of WordPress MCP Adapter 0.7.0: Qwen reads a post, summarizes it inside WordPress, and saves a draft, with permission and API failure checks.