The Brotli out-of-bounds write called Node2Shell and HTTP2Shell (CVE-2026-111497) also reaches the Python Brotli packages and curl builds with Brotli when --compressed is used. On a Windows 11 PC I checked that Python decodes br responses whatever it asks for, that pip-audit now flags it, and that Git for Windows as of October 24 shipped the unpatched Brotli (fixed in 2.56.0.windows.4 on October 26), then updated Node.js.
Ruby 4.0.9, 3.4.12, and 3.3.13 (October 23, 2026) fix the Onigmo regex bugs behind GitLab's CVE-2026-89078, CVE-2026-93577, CVE-2026-97229, and CVE-2026-110264. Any Ruby app that builds a Regexp from outside input should upgrade. Five Ruby versions built under WSL2 show the unpatched ones crashing on the fix PRs' test patterns.
Two days after the php2shell fixes, PHP disclosed CVE-2026-115560 on October 23, 2026, an RCE the October 21 releases do not fix. The three conditions an app must meet, why servers that already set session.upload_progress.enabled=0 need nothing more, what PHP has not published yet, and how to grep your own code.
V4bel's Infinity Core is six bugs in Linux kernel core code (timers, signals, futex, MM, scheduler, SLUB). They were introduced anywhere from 5.7 to 7.2, so Debian 12/13 and stock Ubuntu 24.04 only get the Timer bug, while RHEL picked up Futex and Signal through backports. Per-CVE introduced versions and distro status as of October 22, 2026.
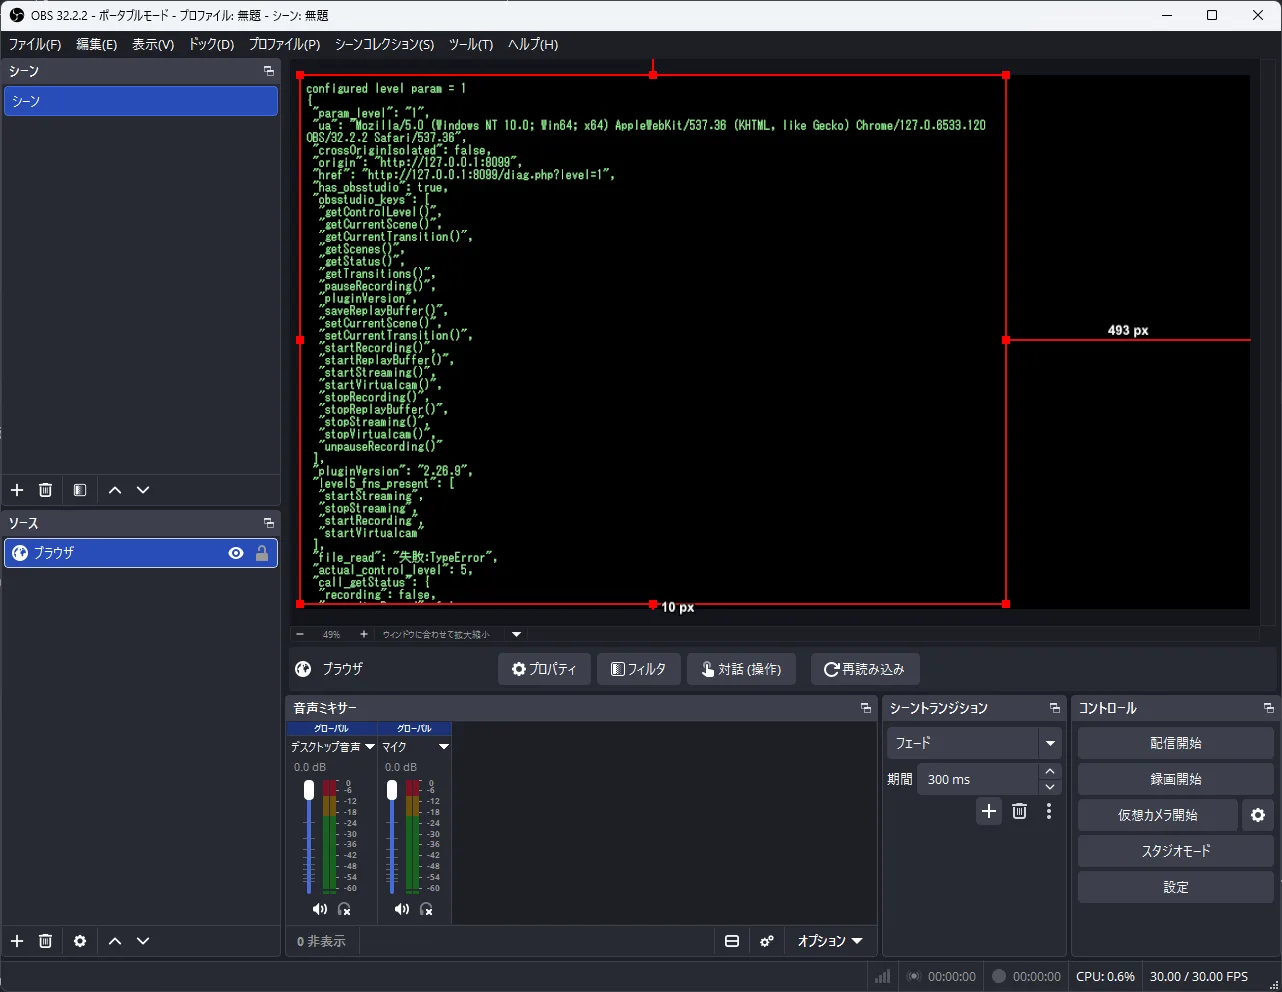
I tested what malicious pages can execute inside OBS Studio's browser source across permissions 0 to 5, obs-websocket, and the disabled CEF sandbox on Windows 11.
On October 21, 2026 PHP patched two unauthenticated RCE flaws (php2shell, CVE-2026-109618/109619). Hours later a self-published page claimed RCE and memory-safety bugs still survive on the patched 8.5.12. Which claims are confirmed, which are unfiled, and what server admins should actually do.
Japanese Prime Minister Sanae Takaichi urged PHP patching on X on October 21, 2026, and took her own website offline. The backstory, from the proposal PDF and official records: her 2018 cybersecurity book from PHP Institute (no relation to the language), the LDP proposal she signed, how it led to Japan's active cyber defense law, and two doctors in a row as Digital Minister.
OpenJDK's out-of-band advisory on October 21, 2026 covers CVE-2026-91403 (CVSS 9.1), eight compromised eMudhra intermediate CAs that Java still trusts. On an M4 Mac mini, OpenJDK 27.0.1 connected through the compromised chains with default settings, and both revocation checking and a patched blocked.certs blocked them.
GitLab's October 21, 2026 critical patch release fixes CVE-2026-110264, a CVSS 10.0 bug in every version since 7.0. How an Org-mode #+TODO: line overflows Onigmo's repeat IDs, which versions to install, why the fix lives in GitLab's bundled Ruby, what to grep in your logs, and a local test showing stock Ruby 4.0.6 is still unpatched.
Apache Tomcat disclosed eight vulnerabilities on October 20, 2026, three rated Important. Which JNDIRealm, HTTP/2 and AJP configurations are affected, checked against the advisories and fix commits, and how to move to 9.0.123, 10.1.61 or 11.0.27.
FoxIO's October 20, 2026 research shows one unauthenticated HTTP/3 connection can OOM or pin the CPU of 7 of 10 tested implementations via QPACK decoding. Fixed versions for quic-go, Cloudflare quiche, lsquic/OpenLiteSpeed, Wireshark and Bun 1.4.4 (October 22), and workarounds for still-unpatched mitmproxy and hyperium/h3.
When the php2shell patch arrived without Remi repository updates, we tested compiling php, php-fpm, and opcache.so from official source in an AlmaLinux 9 container, verified zero-downtime USR2 reloads, bypassed docker kill signal traps, and configured RPM exclusions.