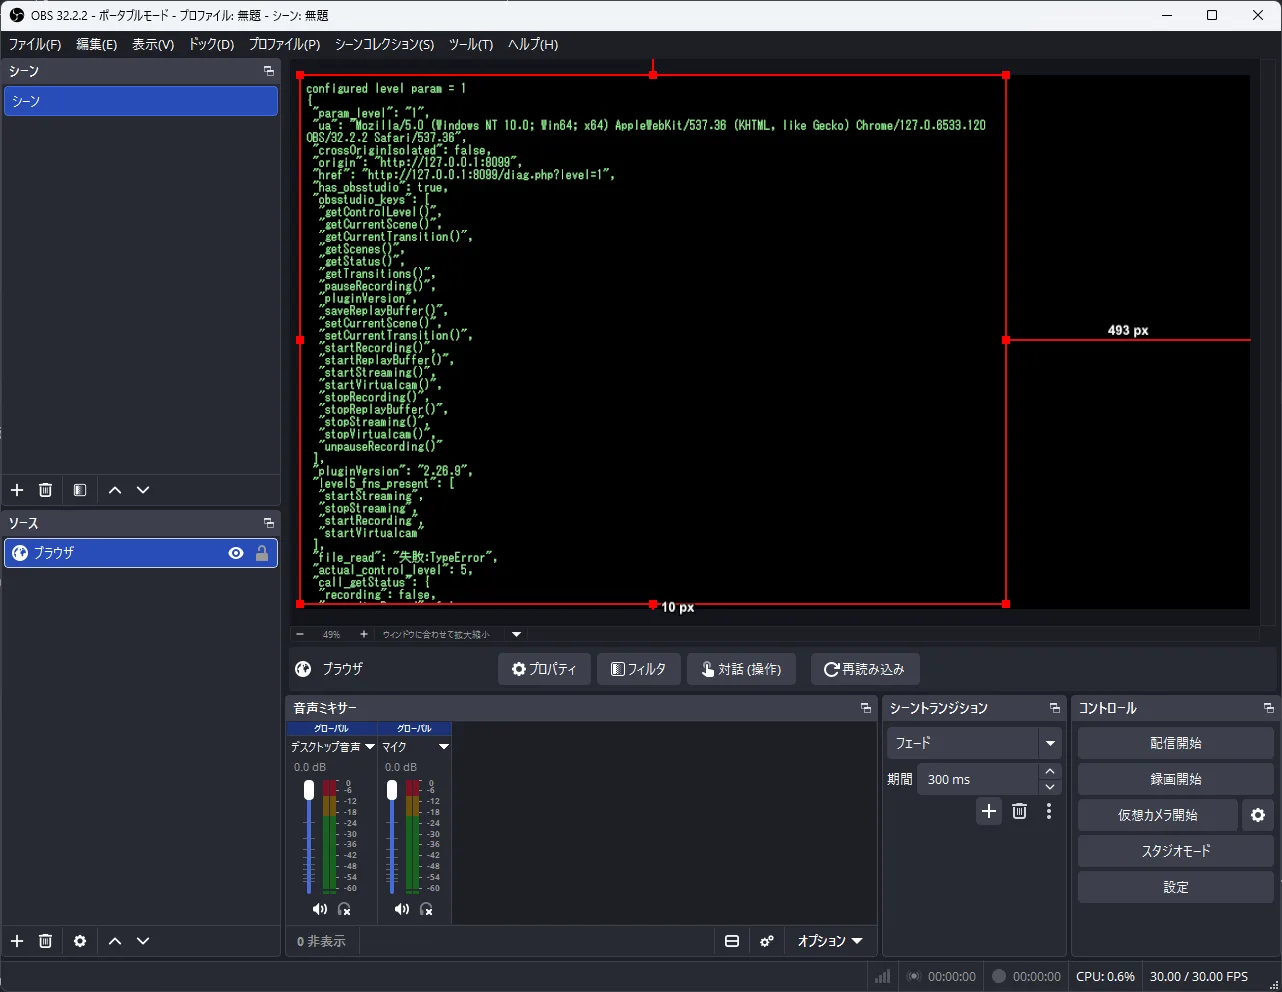
I tested what malicious pages can execute inside OBS Studio's browser source across permissions 0 to 5, obs-websocket, and the disabled CEF sandbox on Windows 11.
In the same week, CISA's KEV catalog gained a Chromium CSS engine UAF, a Roundcube RCE that hid for over a decade, a BeyondTrust RCE abused by ransomware, and a Dagu RCE due to no default authentication. All four require immediate patching.