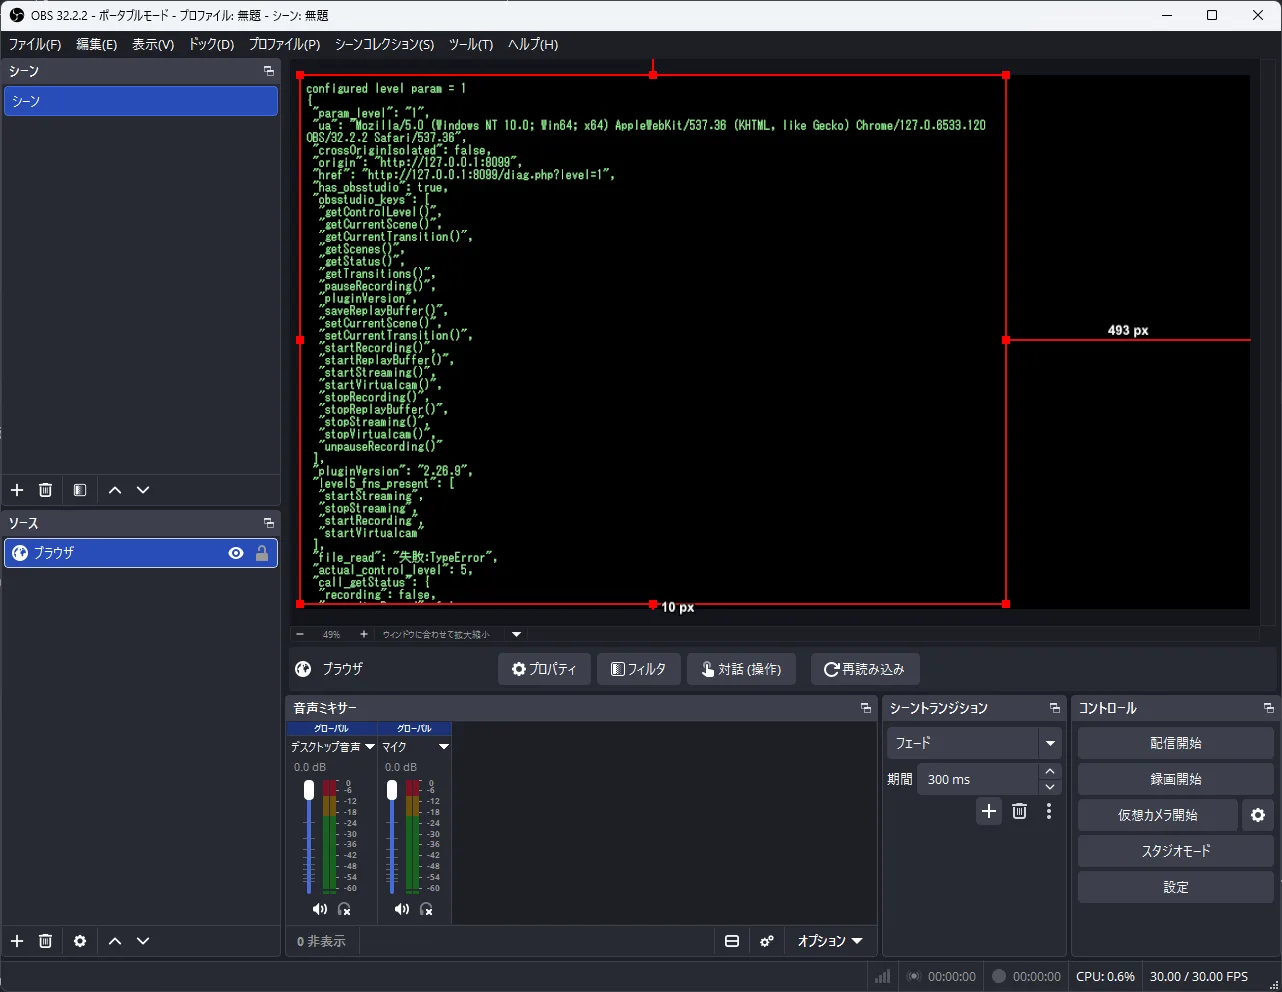
I tested what malicious pages can execute inside OBS Studio's browser source across permissions 0 to 5, obs-websocket, and the disabled CEF sandbox on Windows 11.
On October 21, 2026 PHP patched two unauthenticated RCE flaws (php2shell, CVE-2026-109618/109619). Hours later a self-published page claimed RCE and memory-safety bugs still survive on the patched 8.5.12. Which claims are confirmed, which are unfiled, and what server admins should actually do.
OpenJDK's out-of-band advisory on October 21, 2026 covers CVE-2026-91403 (CVSS 9.1), eight compromised eMudhra intermediate CAs that Java still trusts. On an M4 Mac mini, OpenJDK 27.0.1 connected through the compromised chains with default settings, and both revocation checking and a patched blocked.certs blocked them.
GitLab's October 21, 2026 critical patch release fixes CVE-2026-110264, a CVSS 10.0 bug in every version since 7.0. How an Org-mode #+TODO: line overflows Onigmo's repeat IDs, which versions to install, why the fix lives in GitLab's bundled Ruby, what to grep in your logs, and a local test showing stock Ruby 4.0.6 is still unpatched.
Apache Tomcat disclosed eight vulnerabilities on October 20, 2026, three rated Important. Which JNDIRealm, HTTP/2 and AJP configurations are affected, checked against the advisories and fix commits, and how to move to 9.0.123, 10.1.61 or 11.0.27.
FoxIO's October 20, 2026 research shows one unauthenticated HTTP/3 connection can OOM or pin the CPU of 7 of 10 tested implementations via QPACK decoding. Fixed versions for quic-go, Cloudflare quiche, lsquic/OpenLiteSpeed, Wireshark and Bun 1.4.4 (October 22), and workarounds for still-unpatched mitmproxy and hyperium/h3.
When the php2shell patch arrived without Remi repository updates, we tested compiling php, php-fpm, and opcache.so from official source in an AlmaLinux 9 container, verified zero-downtime USR2 reloads, bypassed docker kill signal traps, and configured RPM exclusions.
A PHP core developer and GMO Flatt Security say disabling session.upload_progress does not stop php2shell. The PHP fix shipped on October 21, 2026 (8.5.12, 8.4.27, 8.3.36, 8.2.35): where to get it and the 8.1-and-older patches, status per distribution channel, how to apply it on shared hosting, apt, dnf, and Docker, and which services went offline.
The October 21, 2026 Node.js security release fixes four HIGH issues, including TLS hostname checks bypassed with alternate IPv4 spellings. I ran the fix commits' test inputs on v24.22.0, v24.22.1, and EOL v25.3.0 on an M4 Mac mini, and list how to upgrade.
PHP will ship fixes for two critical CVSS 9.2 bugs on October 21, 2026 at 14:00 UTC. Leaks call them php2shell (CVE-2026-109618/109619) and tie at least one to session.upload_progress, which is on by default. How to turn it off on shared hosting, php.ini, .htaccess, and .user.ini, and what is official versus leaked.
Analysis of CVE-2026-92392, a High-severity HTTP/2 upload use-after-free in curl 8.12.0 to 8.22.0. We cover the dangling pointer trigger, RCE prerequisites, workarounds, and C maintenance policy.
CVE-2026-99999 (PwnEscape) reveals a CVSS 9.3 flaw in the Linux IPv4 stack enabling KVM escapes. We analyze the vulnerability, hosting provider signup freezes, and remediation.